3281 E. Guasti Rd, STE 700, Ontario, CA 91761
1712 9th Ave SW, Watertown, SD 57201
Could your project team share plans from the field while keeping controlled project information within the right systems? For construction contractors, NIST 800-171 assessment and support should start with that operational question, not a checklist detached from the jobsite.
Security practices need to work across the office, cloud platforms, project workflows, and field devices. The challenge is defining what falls within scope and showing evidence that practices are in place. Unclear documentation or unmanaged field access can make readiness harder to evaluate.
This practical guide explains how to map systems, users, and information flows; gather relevant records; and identify where construction-focused IT or cybersecurity support may help. Before choosing a provider, confirm which NIST revision and contract requirements apply, then ask what the assessment includes. An assessment can identify gaps and next steps, but it does not establish compliance or contract eligibility by itself.
• Define which construction systems, users, and project workflows handle controlled information before setting the assessment scope.
• Check your contract terms to confirm which NIST revision and assessment expectations apply.
• NIST 800-171 assessment and support can help identify evidence gaps and practical next steps, but does not establish compliance or contract eligibility.
• Ask providers to document the scope, method, deliverables, and exclusions. Contact Trinity Networx, LLC to discuss construction IT and cybersecurity support.
A useful readiness review connects applicable security practices to the construction systems and work routines that handle controlled information. It clarifies what applies, where information moves, what evidence is available, and which gaps need attention. Keep the purpose clear: a readiness assessment identifies documented gaps and next steps; it does not guarantee compliance or contract eligibility.
Begin with the contract. Its terms help determine which NIST revision and assessment expectations apply to the work. Verify those details before scoping a review or relying on a checklist. NIST SP 800-171 is part of the broader field of information security standards, but your contract and applicable guidance should shape the specific assessment.
Trace controlled information through an actual project. Where are plans and technical files stored? Who can access them from the office or jobsite? How are files shared with subcontractors, and where are they backed up? Answering these questions helps identify the systems and workflows that need review.
Build the scope from confirmed information flows rather than assumptions. Consider relevant users, computers and mobile devices, cloud services, project file locations, office networks, and field connectivity. Include a system or workflow when it handles, stores, transmits, or protects information within the confirmed assessment boundary. Document office and field access separately when the methods differ.
Construction-focused IT planning can help connect office systems with field access needs. Review IT services for commercial construction to understand the operational demands involved. For NIST 800-171 assessment and support, ask any proposed provider to confirm the NIST-specific scope, evidence expectations, and deliverables in writing. Contact Trinity Networx, LLC to discuss construction IT and cybersecurity needs.
A checklist can reveal gaps, but it cannot establish readiness by itself. For useful NIST 800-171 assessment and support, compare written policies and system records with the way construction teams actually handle project information. First, confirm the revision and assessment expectations in your contract. The NIST SP 800-171 Rev. 2 publication is a reference, not a substitute for checking which requirements apply to your work.
Review these areas against the applicable requirements:
Check user accounts, access records, and how permissions are updated when staff or subcontractor roles change.
Gather device inventories and network documentation for relevant office and field systems.
Identify which project data is backed up and keep records showing how the process works.
Review written procedures and records showing how teams report and handle suspected security events.
Gather current system inventories, access records, security procedures, and relevant network documentation. Then compare those records with day-to-day work. Do office staff and field crews follow the documented steps when they access or share project files?
Documentation should describe practices that are actually in place, not just planned procedures. If a policy calls for controlled access but a field workflow bypasses it, record the difference and identify it for follow-up.
For each gap, record the affected system or workflow, the evidence reviewed, the person responsible, and the next action. A completed checklist is not a compliance determination. Construction-focused IT expertise can help teams review the technology behind these records. Discuss your construction IT and cybersecurity needs with Trinity Networx, LLC.
A provider should understand how project information moves between office staff, field crews, and subcontractors. Ask how the proposed work will account for those workflows instead of assuming your company needs a particular platform or enclave. Trinity Networx, LLC describes its IT services for commercial construction in terms of construction technology and office-to-field operations. That experience can inform the discussion, but it does not mean a service includes a NIST-specific assessment.
Before engaging a provider, put the work in writing. Define the systems and workflows in scope, the assessment method, the evidence expected, the deliverables, and any exclusions. Clarify whether the work covers technical remediation, documentation, ongoing IT management, or formal assessment activities. These are separate tasks, so do not assume one includes the others.
Ask who owns each action, including responsibilities assigned to your internal team. Confirm how findings, assigned owners, and completed changes will be recorded. If field access or project file sharing changes during the work, ask how that affects the agreed scope.
Review relevant CMMC guidance alongside your contract terms, and confirm which NIST revision and assessment expectations apply. Technical support may help address construction IT needs, but it should not be treated as proof of compliance. Confirm whether the provider performs NIST-specific assessment work and whether the deliverables include control mapping or other evidence required by your contract.
Trinity Networx, LLC provides construction-focused IT planning and cybersecurity services. Discuss construction IT and cybersecurity support with the team, including your project needs and whether the proposed scope includes NIST-specific assessment activities.
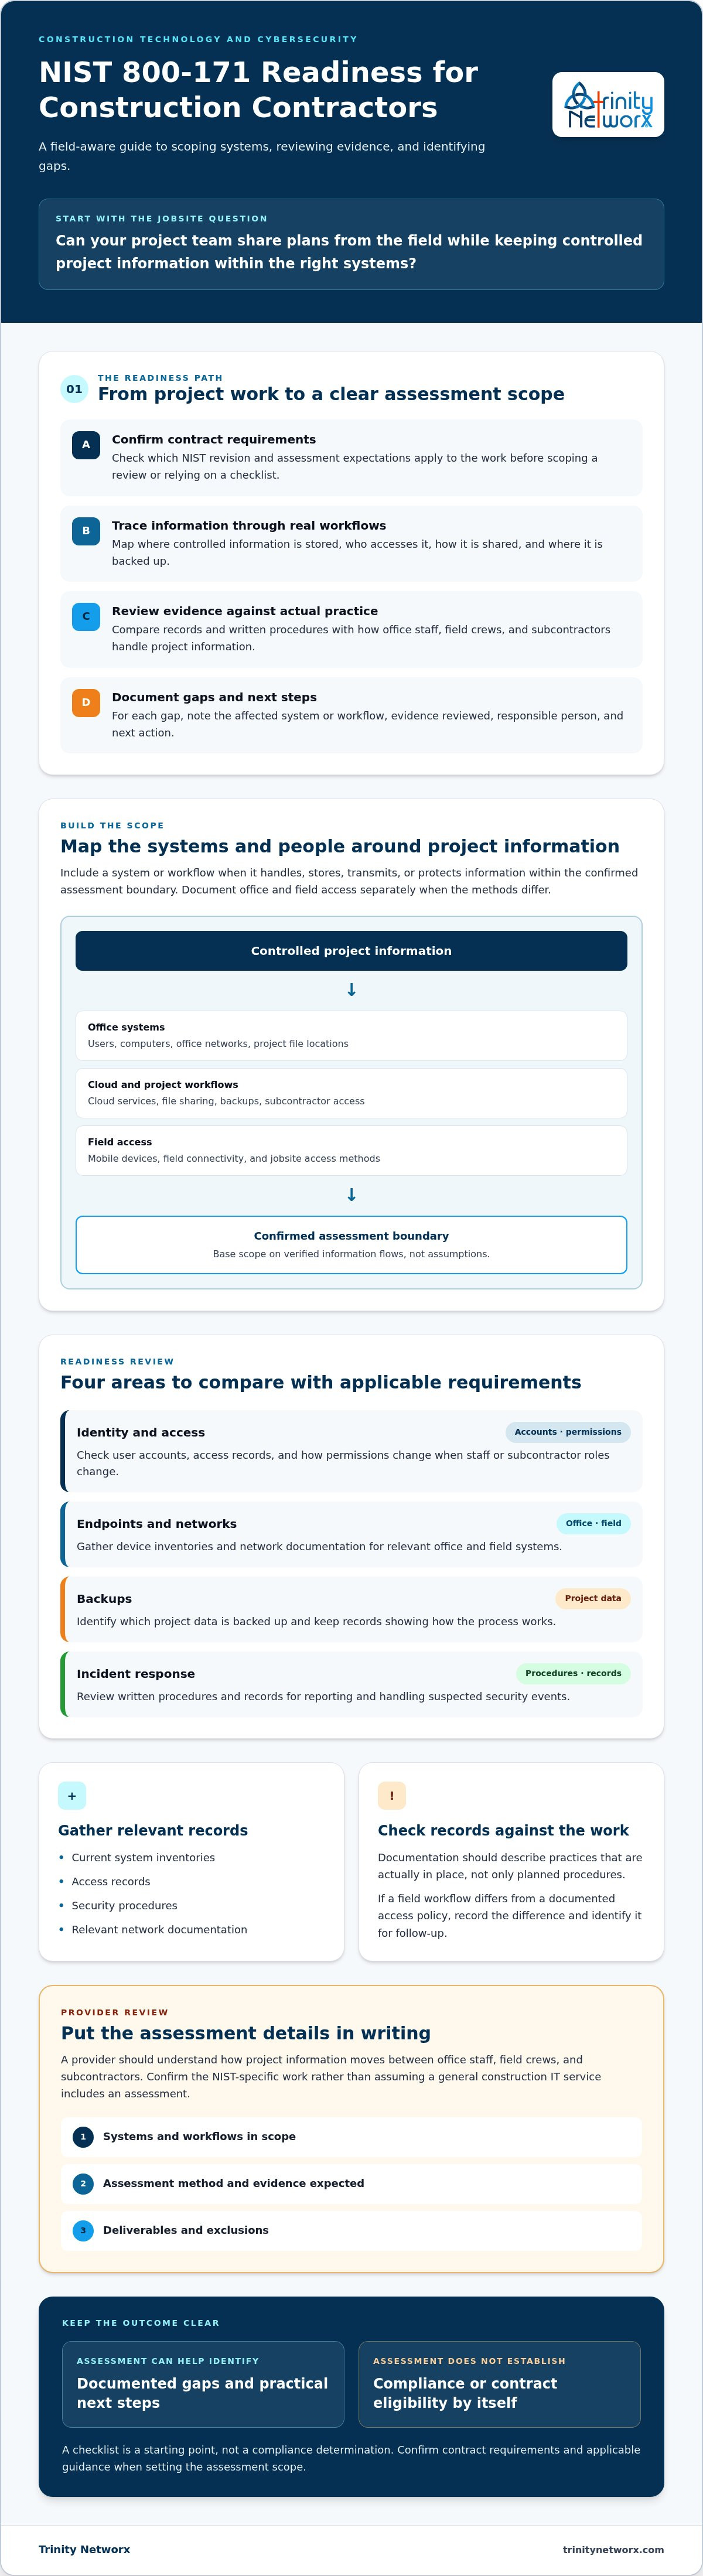
Map where controlled project information moves, compare written records with office and field practices, and assign owners to unresolved gaps. Effective NIST 800-171 assessment and support starts with contract-specific scope, clear evidence expectations, and defined deliverables. A checklist can organize the work, but it cannot establish compliance or guarantee contract eligibility.
Trinity Networx, LLC provides construction-focused IT planning and office-to-field connectivity, along with cybersecurity services. The company also offers a free Security Assessment. Before using it as part of readiness work, ask whether it includes NIST-specific scope, control mapping, or assessment deliverables. Construction businesses in California, Nevada, Arizona, and Utah can also discuss how their office and field operations shape their IT needs.
Contact the team to discuss construction IT and NIST 800-171 support and confirm what NIST-specific services are available. Clear responsibilities and practical technical next steps can help your team prepare with confidence.
No. A NIST 800-171 assessment is not automatically required for every construction contractor. Applicability depends on the contract, the information handled, and the clauses or assessment terms that apply. Before planning assessment work, review your current contract documents and confirm which NIST revision and assessment expectations apply to the project.
An assessment begins by confirming contract expectations and defining which systems, users, and workflows handle controlled project information. The reviewer compares relevant security practices with supporting records, such as access information, system documentation, and procedures, then identifies evidence gaps and follow-up actions. The method and deliverables depend on the agreed scope, so request them in writing before work begins.
Gather current system inventories, user and access records, security procedures, network documentation, and relevant backup or incident-response records. Include office systems and field workflows used to access or share project files. Compare written procedures with how staff and subcontractors actually work, then note missing evidence, action owners, and questions about contract-specific expectations.
No. An IT provider can help review systems, address technical gaps, and support documentation, but an assessment or service engagement cannot guarantee compliance or contract eligibility. Confirm whether the provider offers formal NIST-specific assessment work, what its findings cover, and who owns each follow-up action. Contractors in California, Nevada, Arizona, and Utah can contact Trinity Networx, LLC to discuss construction IT and NIST-specific scope.
Article by
Lance Reichenberger, Ph.D.., J.D. (Candidate)
Dr. Lance Reichenberger is the founder of Trinity Networx, a Southern California technology firm specializing in managed IT services, cybersecurity, network infrastructure, and business technology strategy. With nearly four decades of experience in the IT industry, he works with businesses to improve operational efficiency, strengthen security, and align technology with long-term growth objectives.
Lance focuses on proactive IT management, enterprise wireless infrastructure, cybersecurity integration, and scalable technology solutions for growing organizations throughout Southern California.
The content published on this website is provided for general informational and educational purposes only. Articles may be created, edited, or enhanced with the assistance of artificial intelligence and automation tools under the direction and review of Trinity Networx. While every effort is made to ensure accuracy and relevance, the information provided should not be considered professional, legal, financial, cybersecurity, or technical advice specific to your organization. Businesses should consult directly with a qualified professional regarding their unique environment, compliance requirements, and operational needs. Trinity Networx makes no warranties regarding completeness, reliability, or applicability of the information contained within these articles.
Schedule a brief conversation with Trinity Networx to discuss your business technology needs.
Get a practical roadmap built around your business, your users, your systems, and the technology issues that need attention first.
Put the right technology, support, security, and infrastructure in place so your business can grow, adapt, and move forward with confidence.